Why Pay for Enterprise Antivirus When Windows Already Comes With One?

Because Windows Defender protects your laptop. Enterprise security protects your business.
Defender is excellent for personal use. For a business handling client data, payroll, and operations, “good enough” becomes expensive the day something goes wrong.

1. One Protects a Device. The Other Protects the Entire Business.

Defender is designed for one PC. Enterprise security is designed for your entire fleet.

With Defender, you find out about a threat when you look at that PC.
With Enterprise, you find out before your CEO does.

You get:

  • A Single Pane of Glass: Health, patch status, and threats for every laptop and server — in one dashboard.
  • Policy at Scale: Block USB drives, enforce disk encryption, and push firewall rules to 100 devices in one click. No desk-to-desk.
  • Incident Storyline: Defender says “threat found.” Enterprise says “User opened a phishing attachment 3 days ago, here is how it moved laterally, and here is exactly what to contain.”

2. Modern Attacks Don’t Look Like Viruses Anymore

Free antivirus asks: “Do I recognize this file?”

Modern attacks ask: “Can I use your legitimate tools against you?”

Ransomware today doesn’t always drop a .exe. It uses PowerShell, Excel macros, and remote management tools to encrypt files at 2 AM.

Enterprise security with EDR (Endpoint Detection and Response) watches behavior:

“Why is a process suddenly encrypting 10,000 files and deleting backups?”

It then automatically kills the process, isolates the device from the network, rolls back the files, and sends an alert to IT. Defender alone will often just quarantine one file — after the damage is done.

3. Auditors, Clients, and Insurers Don’t Accept “We Have Defender”

If you store any customer data, you will eventually be asked:

“What is your EDR solution? Do you have 24/7 monitoring? Can you produce 90 days of centralized logs?”

For ISO 27001, SOC 2, PDPA compliance, and cyber insurance, “Windows Defender” is not an acceptable answer. A claim can be denied for not having enterprise-grade controls.

Enterprise security gives you audit-ready reports, compliance mapping, and a vendor who shares liability and provides forensic support.

4. You’re Not Buying Antivirus. You’re Buying a Security Stack.
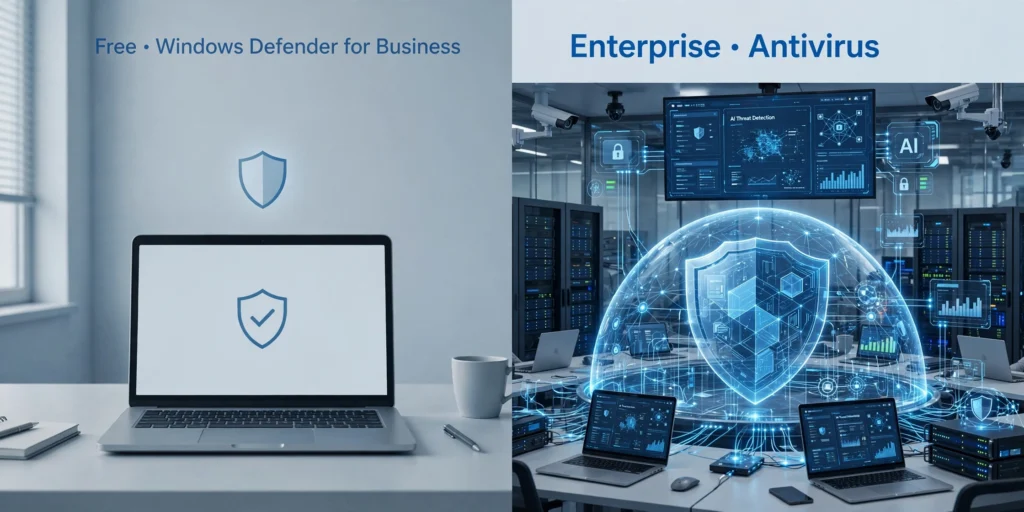
What is marketed as “Enterprise AV” is now 5 products in 1:

  1. Next-Gen Antivirus + Anti-Ransomware with AI and rollback
  2. Device & Firewall Control across the fleet
  3. Email & Phishing Protection that catches CEO fraud before it hits the inbox
  4. Application Control to stop unapproved software
  5. Managed Threat Hunting — a team that will actually respond at 3 AM on your behalf

Defender gives you number one. Businesses need all five.

5. The Hidden Cost of Free

Free has no invoice, but it has a time cost.

Without central management, your IT team spends hours manually checking devices, cleaning infections one by one, and building reports for management.

A quick calculation:
4 hours/week on endpoint issues x 52 weeks = 208 hours/year lost.

An enterprise suite for 20 users is typically less than the cost of one minor IT incident, let alone the cost of a week of downtime.

Windows Defender (Built-in) Enterprise Security (EDR)
Best ForPersonal use, single deviceBusiness with 10+ devices and customer data
VisibilityOnly on that deviceFull fleet visibility + alerts to IT
If Breached Manual investigationAuto-containment, rollback, and forensic report
ComplianceNo reportingAudit-ready reports for clients & insurers
SupportMicrosoft forumsDedicated incident response team


The Bottom Line

Think of it like fire safety.

Windows Defender is the fire extinguisher that comes with your building. It’s essential and you should have it.

Enterprise security is the full system: smoke detectors, sprinklers, central monitoring station, and the fire brigade on call.

You wouldn’t protect a warehouse full of inventory with just one extinguisher.

Free = Your IT guy (or you, even though you constantly open excel files using Word) spends 4 hours per week fixing one-off infections, and manually spending previous work hours to fix it.

If your business can afford to be offline for a week and explain a data leak to clients, Defender is sufficient.

If it can’t, that’s what you’re paying for — continuity, visibility, and someone to call when it matters.
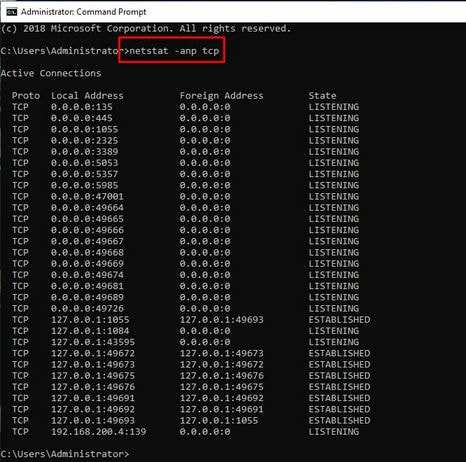
Allowing processes blocked by firewall

01. List all listening TCP ports with “netstat -anp tcp” in administrator’s CMD.

netstat to list open tcp ports

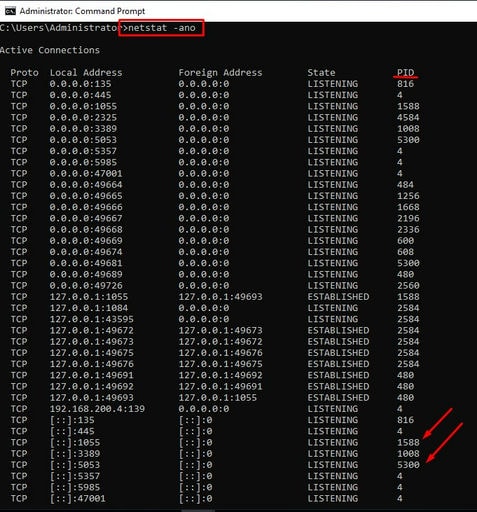
02. Find PID associated with open ports requiring inbound connections.

find PID for process owner

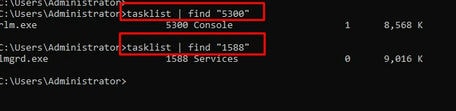
03. Pipe tasklist to find to locate process owner’s name.

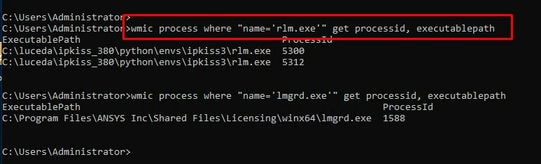
04. User wmic to locate full executable paths of all processes you would like to pass Windows firewall.

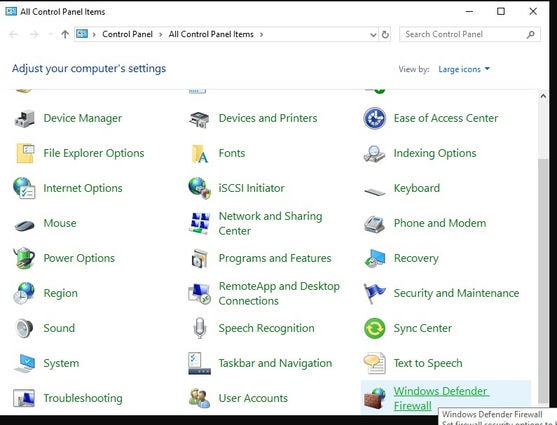
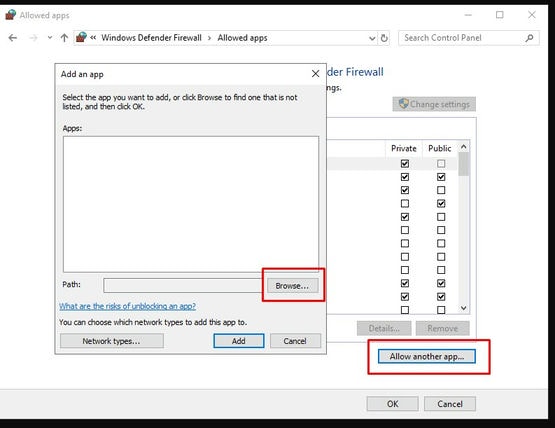
05. Go to Control Panel, All Control Panel Items and select Windows Firewall.

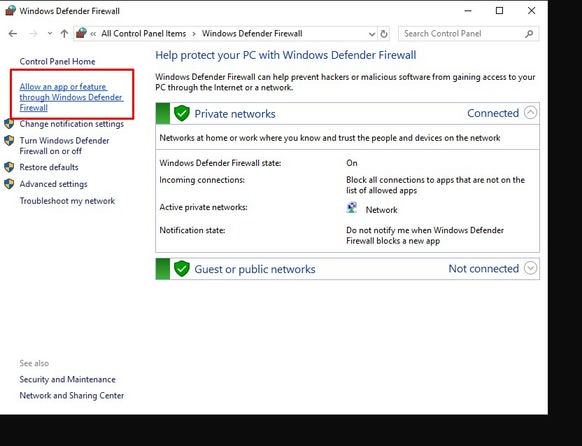
06. Select Allow an app or feature through WIndows Defender Firewall.

GUI allow program through firewall

07. Select Allow another app.

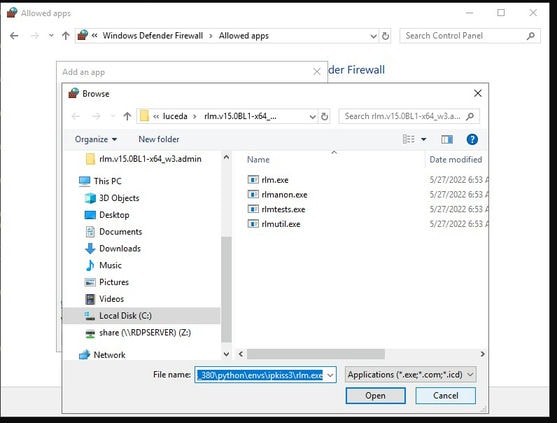
08. Copy from command line process’ full path, paste and click Open.

paste process full path

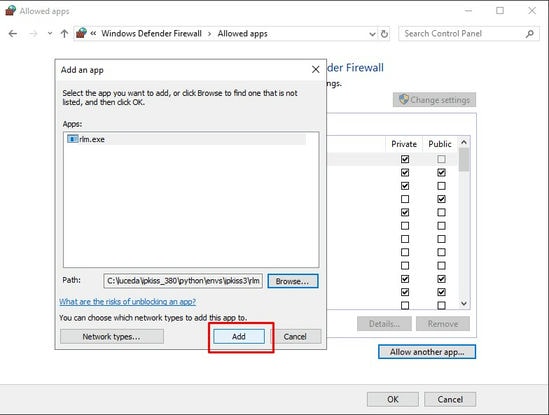
09. Click Add to add the program. Repeat process for all other running processes that are blocked.

Some applications may dynamically assign ports to listen to for inbound connections, adding the program itself will prevent allowing static ports in while blocking all others used by the process.

Exchange vs Traditional Mail System

Full featured Cloud Solution

Some companies may not foresee the implication when using older POP3 and IMAP mail system – disgruntled employees may remove critical information in their email mailbox and nobody may be aware of it, data get lost when system crashes and data inconsistencies on multiple devices.

Comes Office 365 with it range of data from mailbox, Onedrive, Sharepoint sites and even Teams messages, your retention policy is applied to all users’ content and can be placed indefinitely on legislation hold, making such information available should the need arises.

Access to any mailbox can be simply be assigning access permission instead of copying/moving of email psts all over the place.

Losing your emails due to system failures and crashes will not be an issue as with Exchange email, all is required is just to setup your email account on another system and resync all mailbox to the new device with everything intact.

A large portion of email compromise is due to lack of multilayer authentication. A successful bruteforce attack will enable a hacker unrestricted access to your mailbox thereafter. MFA/2FA allows for an additional layer of security through code verification on an authenticator app on owner’s mobile device.

In traditional Cpanel hosting, 2-factor authentication is only available for webmail access but not within Outlook as there is no native support nor third party application for it yet.

The migration process may be tedious but we are able to provide you the full support required.

Malware Removal Solution

Malware is a huge issue when everyone is connected virtually in someway.

It can also be a ransomware that encrypt your system and allow remote access to your system and your corporate network.

Most come with a payload to spread itself to other users in your environment or associates in your contact list.

Removal is difficult as some malwares are rootkits, meaning they start themselves as a system service.

Ever get those anti-virus prompt of virus removal that keeps coming up after removal? That is likely a rootkit malware. Usually this will require creating a boot disk and using an image from the antivirus company that scan through your hard disk without starting Windows.

Malware Removal then System Repair? Why not do both with just one software?

There may be system file damage, traces of temp files of viruses/spywares waiting to reload and system registry cleaning up to be done.

Instead of using a magnitude of software to clean and optimize your, why no just use software to achieve this.

Powerful technology that secures and safely repairs any PC to an optimized state. It’s the one software any PC user ever needed.

Get the complete system solution here:

  • Remove malware threats
  • Detect dangerous websites
  • Restore max performance
  • Free precious disk space
  • Replace damaged WinOS files

Don’t take any chances, repair the damage NOW Download Here!

Malwares in the wild now includes Nevada ransomware, Python RAT, HeadCrab malware, PlugX malware with the last one being quite rampant.

We provide virus and malware removal service, however note that decrypting ransomware is not possible.

While generic routers don’t differentiate malicious outbound traffics from legit ones, a good hardware firewall at your network perimeter can generally detect suspicious activities on endpoints.

You can contact us for firewall solution catered to your environment. If you require malware removal service, please contact us at +65 96944441.

Identifying Phishing and Mitigating It

Most phish attempts start from obtaining users’ passwords then proceed to downloading of payloads so that the end systems can be controlled remotely.

Attacker subsequently gathers info to propagate infection, disables security and attempts privilege escalation (eg. dumping payloads to vulnerabilities within the network). It may also includes encrypting of critical data (typical ransomware attack) then requesting payment to decrypt them.

The result of a successful phishing attack is usually targetted at causing financial losses but its impact entails far more damage.

Impersonating colleagues

One scenario may be a junior staff receiving instruction from their manager claiming to be overseas and instructing his/her staff to urgently remit money to a bank account due to a last minute agreement/purchase.

In this scenario, the manager account is compromised and the pepertrator is monitoring the account and send the phishing email using similar signature and writing style to trick the recipient to pay an unknown party.

The attempt would be for a amount that is large enough but yet not trigger a phone call to the manager.

Impersonating suppliers

Another scenario would be, when a customer’s email account is compromised, it is monitored for correspondence between the compromised account and his/her suppliers.

The perpetrator then registers a misspelled domain (1 as L or I, I as L) that is similar to domain of one of the suppliers that has bigger transactions with the customer.

Subsequently, a phishing email is then sent to the compromised account claiming to be from the supplier using the mispelled domain registered. The phisher the impersonate as the supplier, requesting any upcoming payments to be sent to a different bank account (under a different name) citing issues with their bank.

If successful, both customer and supplier will suffer financial loss (one from not getting paid and the other from paying to an unknown party).

Mitigation

In above scenarios, enabling MFA – where logins are challenged with a code sent to registered mobile number or via authenticator, may alleviate the issue.

MFA may be also be configured to be required only when users are signing in from unfamiliar IP addresses outside of their corporate network.

It would be ideal to prevent getting compromised from the start by implementing firewall web filters preventing users from reaching a phish site.

There are also phishing simulation (Defender for Business for Microsoft 365) that will simulate attacks to train users detect emails that looks like phishing attempts. (For users that fail the simulation, they may be requested to go for a friendly coffee session – aka retraining on how to detect phishing.)

IT department may also geo-target the authentications to be allowed only from within a fixed number of geolocations and monitor audit logs for malicious attempts and react accordingly.

Phishing attempts usually start with a forged email with a link for users to authenticate and then initiates an install of malware to the system.

Phishing/malware links can be blocked/prevented using a mix of firewall web-filtering and application layer control.

Don’t have MFA/2FA? Synchronization of emails taking too long? – contact us to sign up for Office 365.

If you require reviewing or securing your network, feel free to contact us. We will be happy to assist you.

A Microsoft-based phish simulation tool is available with Microsoft Defender Plan 2. It is ideal for administrators that would like to run simulations prior to conducting training to users.

Wifi6 with wireless controller

The Ubiquiti UniFi Network Controller is a powerful software platform that allows you to manage your entire network from a single, easy-to-use interface. When paired with the Ubiquiti LR6 Series access points, it provides a high-performance and scalable wireless network solution that can meet the needs of even the most demanding environments.

The Ubiquiti UniFi Network Controller is designed to simplify network management, allowing you to easily configure and monitor your entire network from a central location. With features such as real-time network monitoring, traffic analysis, and customizable alerts, you can ensure that your network is running smoothly and efficiently at all times.

The Ubiquiti LR6 Series access points provide exceptional wireless performance, with support for high-speed 802.11ac Wi-Fi and the latest MIMO technology. They also feature a sleek, minimalist design that blends seamlessly into any environment, making them ideal for both commercial and residential installations.

When used together, the Ubiquiti UniFi Network Controller and Ubiquiti LR6 Series access points provide a complete and powerful wireless networking solution that can meet the needs of businesses of all sizes. With advanced features such as guest access, VLAN support, and seamless roaming, you can ensure that your users have the connectivity and security they need to be productive.

Overall, the Ubiquiti UniFi Network Controller with Ubiquiti LR6 Series access points is a powerful and reliable wireless networking solution that can provide exceptional performance and ease-of-use. Whether you are looking to upgrade your existing wireless network or deploy a new one from scratch, this solution can help you achieve your goals and meet the needs of your users.

On-prem management option

Run a dockerized Unifi network controller on-premise with Synology NAS. Manage your site network without the need for cloud key. Set configuration and install updates with a single click.