Business Email Compromise doesn’t start with hacking. It starts with a single compromised mailbox.
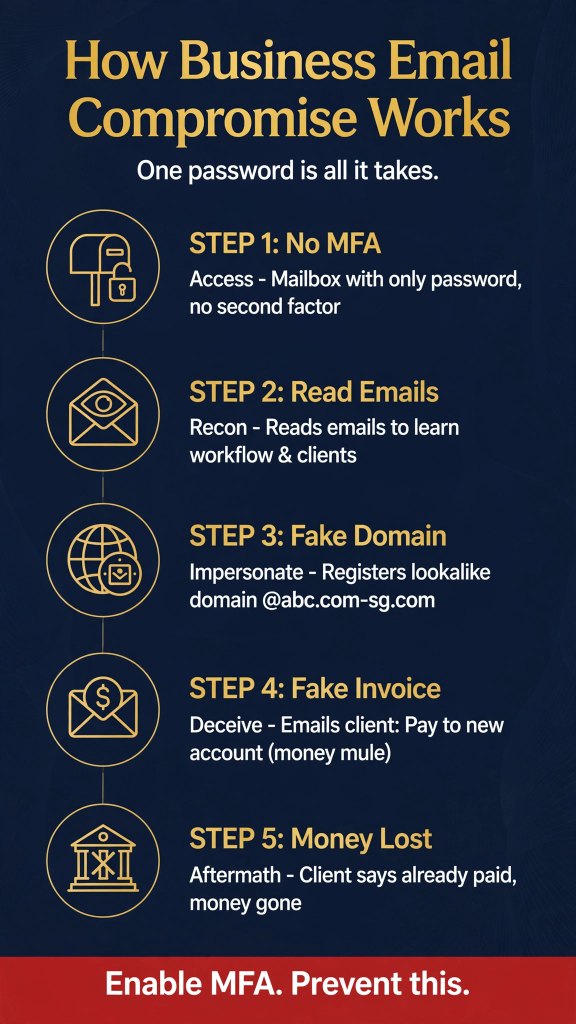
How it happens:
- Initial Access: The attacker gains access to a mailbox protected only by a password, with no Multi-Factor Authentication (MFA).
- Reconnaissance: They monitor email threads to understand invoicing workflows, client relationships, and payment patterns.
- Impersonation: They register a deceptively similar domain to the compromised account.
- Execution: They impersonate the victim and instruct clients to remit payment to a new bank account controlled by a money mule. Alternatively, they impersonate the business owner to authorize an urgent, fraudulent transfer from the accounts department.
The Result:
The business attempts to recover payment, only to learn the client has already paid — to the attacker. Or, funds have already been wired to an untraceable account based on a seemingly legitimate internal request.
MFA is not an IT feature. It is your last line of defense.